AI pentesting · Web security intelligence
Your site looks fine. Look underneath.
Everything running beneath the page, found, tested like an attacker would, and proven.
Free. No account. Report in 15 seconds. See a sample report
What's underneath
One page load. Six layers of exposure.
SURFACE
The surface
This is all your visitors, and most scanners, ever see. A site that looks fine, loads fine and passes a glance. Keep scrolling to peel it back.
The full breadth
Scanner. Investigator. Pentester. Auditor.
Eight capability areas and 69 features, all working from the same findings. Start with a free 15 second scan and go as deep as you need.
Surface scan
Eight layers on one page in about 15 seconds. No account.
HOVER OR TAP A BRANCH
In practice
The things other scanners walk straight past.
An analyst that never stops pulling threads.
Watch the agent reason through scripts, tag managers and domains in real time. It becomes your audit trail.
Built with AI? Check what it shipped.
Open databases and leaked keys in generated apps.
anon key in main.js
RLS policy missing
fix: enable row level security
Audit-ready by default.
Findings mapped to the controls your auditor asks for.
Confirmed exploits, not maybes.
Your scan finds the targets. Specialist tools then attempt real exploitation inside an isolated sandbox, and every confirmed finding ships with proof.
- Consent-gated: only targets you approve
- Payload, request and response attached as evidence
- Its own Pentest Score and standalone PDF
- Confirmed exploits also lower your overall grade
sqlmap
SQL injection
Detects and exploits injection flaws, then proves impact by showing what the database gives up.
boolean / time / union
dalfox
Cross-site scripting
Analyses parameters and fires context-aware payloads to confirm reflected and DOM XSS.
reflected / DOM
commix
OS command injection
Finds inputs that reach the operating system shell and confirms execution.
classic / time-based
nuclei
SSRF, XXE & exposure
Out-of-band callbacks confirm SSRF and XXE, plus template checks for exposures and misconfigurations.
out-of-band / templates
ffuf
Hidden parameters
Fuzzes for undocumented parameters and routes the scan did not see on the surface.
paths / params
jwt_tool
Token weaknesses
Attempts to crack weak JWT signing secrets in the tokens your app issues.
weak secrets
Specific, scored, shareable.
Every scan produces a graded report with real evidence, an AI summary and a public link you can send to anyone. No login needed to try it. This one is a real scan, all 1,238 findings of it.
Security Score
Critical - immediate action needed
ginandjuice.shop
just now
Confirmed XSS: searchTerm
DOM verification successful for param searchTerm (JS-context AST)
angularjs 1.7.7 - CVE-2019-10768
14 known CVEs · /resources/js/angular_1-7-7.js
Missing Content-Security-Policy header
Also missing HSTS · on 48 of 48 URLs checked
No DMARC record found
No SPF record either · email spoofing risk
AI Summary
The most serious problems - missing HSTS and CSP headers and several high-risk AngularJS vulnerabilities - affect every page (48 of 48) and the majority of the site's JavaScript.
A real Enterprise scan of ginandjuice.shop, PortSwigger's deliberately vulnerable demo store.
Built for
From a weekend build to a regulated business.
Pricing
Start free. Scale when you need to.
Free for individual page checks. Paid plans unlock full AI agent investigations, scheduled scans, and compliance reporting - at a fraction of enterprise scanner costs.
Free
- 1-page scan per submission
- All 8 scan layers
- Vibe-coded platform security scan (Supabase, Lovable, Base44 & more)
- AI executive summary
- OWASP Top 10 coverage checklist
- Scan history in your account
- Re-scan and delete anytime
- Shareable public link
- Visual scoreboard dashboard
Starter
- Full AI agent investigation
- Up to 50 pages per scan
- Per-finding remediation guidance
- Priority Remediation Plan (top fixes, AI-written, exportable PDF)
- AI assistant chat
- DNS & SSL/TLS security analysis
- Subdomain takeover detection
- Lookalike domain monitoring (typosquat alerts)
- Open port & service discovery for IP scans
- PDF evidence export
- Scheduled recurring scans
- Scan comparison reports
- Email alerts for new criticals
Pro
- Everything in Starter
- Up to 200 pages per scan
- ISO 27001 / SOC2 / NIS2 / DORA / LGPD / PCI DSS / NIST CSF / EU CRA control mapping
- Remediation tracking
- Team access and finding assignment
- Slack and webhook notifications
- API access
- Audit evidence packages
- Audit activity log
- White-label PDF branding
Enterprise
- Everything in Pro
- Active Security Testing (DAST)
- Independent Active Testing Score
- AI Pentesting (exploitation-confirmation testing)
- Forced browsing, CORS, reflected-input probes
- API endpoint discovery & testing (REST, GraphQL, SOAP)
- Authenticated scan mode (session capture)
- Enable active testing via API / MCP
- Expert Mode & Scan Profiles (rate limits, crawl scope, per-tool pentest control)
- Priority support
The Decloak Journal
Security news & platform updates.
Stories from around the web security world, plus release notes and changes to Decloak itself.
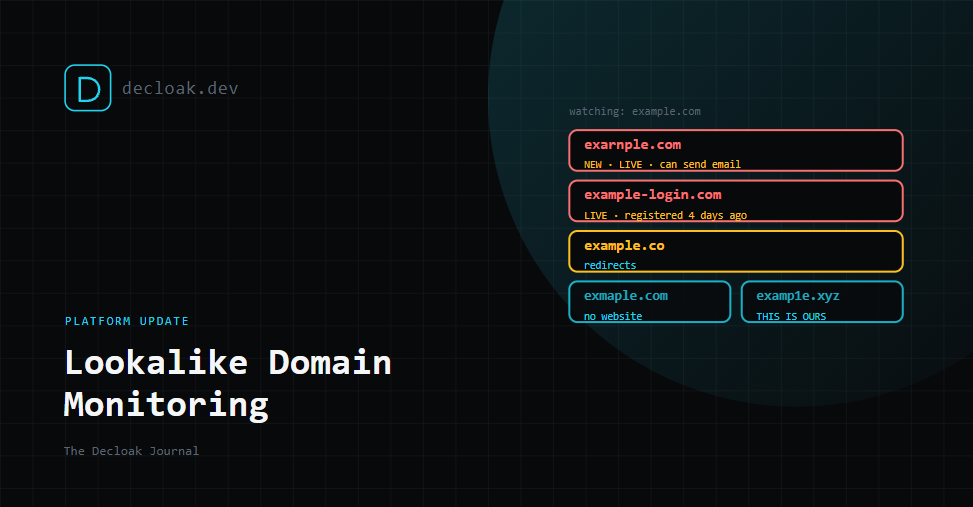
Lookalike Domain Monitoring Is Live: Find Out When Someone Registers a Copy of Your Domain
Your scans only see your own site, but a phishing page imitating your brand lives on someone else's domain. Decloak now checks up to about 250 realistic variations of your domain every day and tells you when one is registered and serving a live website.
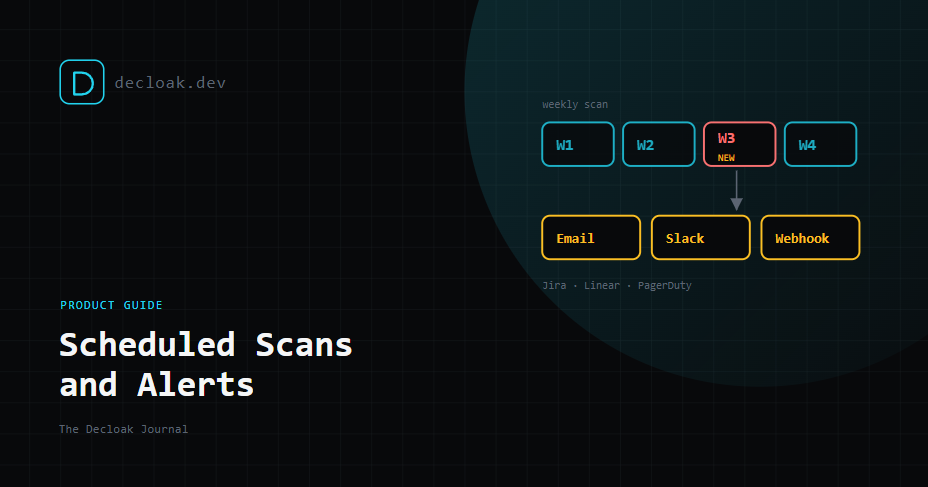
Set It Once: Scheduled Scans, Email Alerts, Slack and Webhooks in Decloak
Your site changes when nobody deploys: certificates expire, tags get published, a plugin auto-updates, a new CVE lands against software you already run. Scheduled scans and alerts turn Decloak from something you remember to run into something that tells you. Here is how to set it up, and what to expect from it.
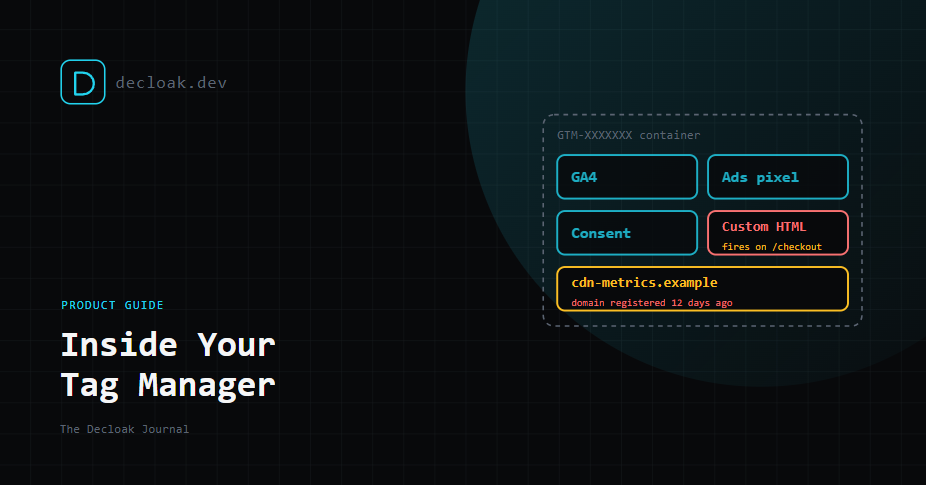
Your Tag Manager Can Change Your Live Site Without a Deploy. Here's What Decloak Checks Inside It
Anyone who can publish in Google Tag Manager can put JavaScript on every page of your site, with no code review and no deploy. Attackers know this. Here is why tag managers are a favourite hiding place for card skimmers, and what Decloak's tag manager checks show you.
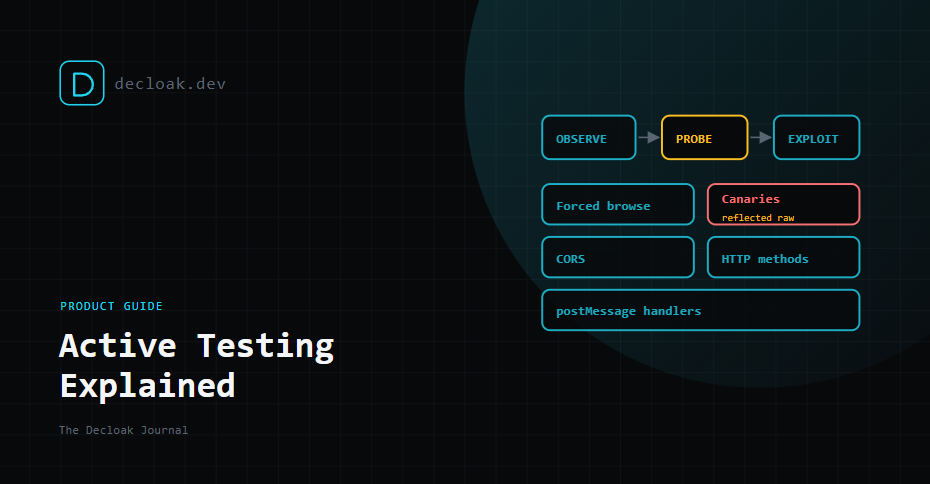
Active Testing Explained: What Decloak's DAST Layer Probes, and What It Leaves Alone
A passive scan watches what your site does. Active Testing asks it questions: it requests paths nobody links to, sends harmless markers into inputs and checks how the server answers. Here is what each probe does, how it stays non-destructive, and where it stops.
Try it now