AI pentesting · Web security intelligence
Your site looks fine. Look underneath.
Everything running beneath the page, found, tested like an attacker would, and proven.
Free. No account. Report in 15 seconds. See a sample report
From our users
In their words.
“The level of detail is impressive: headers, scripts, DNS, libraries, all explained in plain language with clear fixes... I asked for reports in Dutch, and two weeks later PDF exports came in 11 languages.”
Mark S.
Freelance web designer, Belgium
“I especially like the explicit OWASP Top 10:2025 coverage checklist. It removes the guesswork around what was checked, what came back clean, and what could not be tested.”
Kris R.
@Kris_R
“What makes Decloak remarkable isn't just the number of features. It's how they've made sophisticated security capabilities accessible and actionable for someone like me.”
Mark B.
Seven years in the cybersecurity industry
“It gives me specific places to look and questions to ask, which is much more actionable than simply wondering whether I have overlooked something.”
Anthony R.
Vibe coder
“Decloak has earned a real place in our stack. We use it as a strong security-testing evidence source with human review... both the product depth and the team's responsiveness have been excellent.”
Eddie
Runs website security assessments
“This tool has significantly streamlined my workflow... It saves me 3-4 hours of work time. The UI is excellent, and the scanner's transparency is impressive; it provides clear, verifiable evidence for every vulnerability detected.”
King Server
Senior Cybersecurity Analyst
“Decloak does not replace a skilled professional penetration tester, nor should any automated platform claim to... But professional penetration testing can also cost thousands or tens of thousands of dollars. For the price point here, the breadth and depth of what Decloak provides is excellent!”
haterfactory2
Former white hat hacker
“I really love this tool! Thank you for shipping it to us!”
user901
@user901
What's underneath
One page load. Six layers of exposure.
SURFACE
The surface
This is all your visitors, and most scanners, ever see. A site that looks fine, loads fine and passes a glance. Keep scrolling to peel it back.
The full breadth
Scanner. Investigator. Pentester. Auditor.
Eight capability areas and 73 features, all working from the same findings. Start with a free 15 second scan and go as deep as you need.
Surface scan
Eight layers on one page in about 15 seconds. No account.
HOVER OR TAP A BRANCH
In practice
The things other scanners walk straight past.
An analyst that never stops pulling threads.
Watch the agent reason through scripts, tag managers and domains in real time. It becomes your audit trail.
Built with AI? Check what it shipped.
Open databases and leaked keys in generated apps.
anon key in main.js
RLS policy missing
fix: enable row level security
Audit-ready by default.
Findings mapped to the controls your auditor asks for.
Confirmed exploits, not maybes.
Your scan finds the targets. Specialist tools then attempt real exploitation inside an isolated sandbox, and every confirmed finding ships with proof.
- Consent-gated: only targets you approve
- Payload, request and response attached as evidence
- Its own Pentest Score and standalone PDF
- Confirmed exploits also lower your overall grade
sqlmap
SQL injection
Detects and exploits injection flaws, then proves impact by showing what the database gives up.
boolean / time / union
dalfox
Cross-site scripting
Analyses parameters and fires context-aware payloads to confirm reflected and DOM XSS.
reflected / DOM
commix
OS command injection
Finds inputs that reach the operating system shell and confirms execution.
classic / time-based
nuclei
SSRF, XXE & exposure
Out-of-band callbacks confirm SSRF and XXE, plus template checks for exposures and misconfigurations.
out-of-band / templates
ffuf
Hidden parameters
Fuzzes for undocumented parameters and routes the scan did not see on the surface.
paths / params
jwt_tool
Token weaknesses
Attempts to crack weak JWT signing secrets in the tokens your app issues.
weak secrets
Specific, scored, shareable.
Every scan produces a graded report with real evidence, an AI summary and a public link you can send to anyone. No login needed to try it. This one is a real scan, all 1,238 findings of it.
Security Score
Critical - immediate action needed
ginandjuice.shop
just now
Confirmed XSS: searchTerm
DOM verification successful for param searchTerm (JS-context AST)
angularjs 1.7.7 - CVE-2019-10768
14 known CVEs · /resources/js/angular_1-7-7.js
Missing Content-Security-Policy header
Also missing HSTS · on 48 of 48 URLs checked
No DMARC record found
No SPF record either · email spoofing risk
AI Summary
The most serious problems - missing HSTS and CSP headers and several high-risk AngularJS vulnerabilities - affect every page (48 of 48) and the majority of the site's JavaScript.
A real Enterprise scan of ginandjuice.shop, PortSwigger's deliberately vulnerable demo store.
Built for
From a weekend build to a regulated business.
Pricing
Start free. Scale when you need to.
Free for individual page checks. Paid plans unlock full AI agent investigations, scheduled scans, and compliance reporting - at a fraction of enterprise scanner costs.
Free
- 1-page scan per submission
- All 8 scan layers
- Vibe-coded platform security scan (Supabase, Lovable, Base44 & more)
- AI executive summary
- OWASP Top 10 coverage checklist
- CDN & WAF detection (block pages are never graded)
- Scan history in your account
- Re-scan and delete anytime
- Shareable public link
- Visual scoreboard dashboard
Starter
- Full AI agent investigation
- Up to 50 pages per scan
- Per-finding remediation guidance
- Priority Remediation Plan (top fixes, AI-written, exportable PDF)
- AI assistant chat
- DNS & SSL/TLS security analysis
- Subdomain takeover detection
- Lookalike domain monitoring (typosquat alerts)
- Firewall allowlist header for blocked scans
- Open port & service discovery for IP scans
- PDF evidence export
- Scheduled recurring scans
- Scan comparison reports
- Email alerts for new criticals
Pro
- Everything in Starter
- Up to 200 pages per scan
- ISO 27001 / SOC2 / NIS2 / DORA / LGPD / PCI DSS / NIST CSF / EU CRA control mapping
- Remediation tracking
- Team access and finding assignment
- Slack and webhook notifications
- API access
- Audit evidence packages
- Audit activity log
- White-label PDF branding
- PDF reports in your language (11 languages)
Enterprise
- Everything in Pro
- Active Security Testing (DAST)
- Independent Active Testing Score
- AI Pentesting (exploitation-confirmation testing)
- Forced browsing, CORS, reflected-input probes
- API endpoint discovery & testing (REST, GraphQL, SOAP)
- Authenticated scan mode (session capture)
- Enable active testing via API / MCP
- Expert Mode & Scan Profiles (rate limits, crawl scope, per-tool pentest control)
- Priority support
The Decloak Journal
Security news & platform updates.
Stories from around the web security world, plus release notes and changes to Decloak itself.
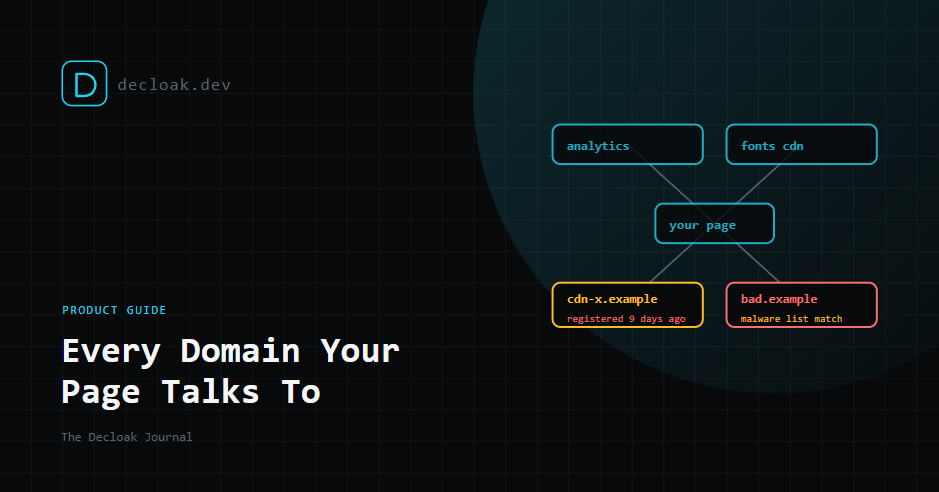
Your Pages Talk to Domains You've Never Heard Of. Here's How Decloak Maps and Checks Every One
Load almost any modern web page and it quietly contacts dozens of other domains: analytics, fonts, ads, chat widgets, payment tools and whatever those tools load in turn. Each one can run code on your site. Here's how Decloak maps them, checks them against threat data, and flags the ones that deserve a closer look.
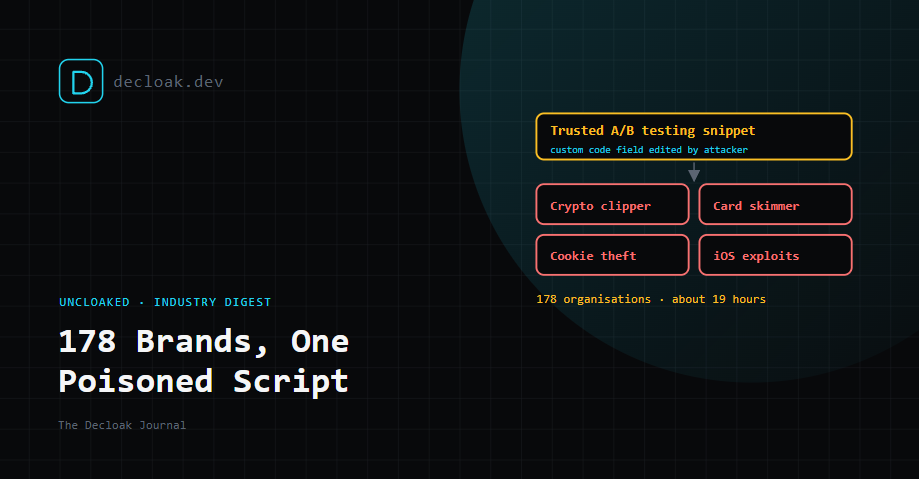
Uncloaked: The Optimizely Attack Hit 178 Organisations That Didn't Change a Line of Their Own Code
For about 19 hours, malicious code delivered through the Optimizely A/B testing platform skimmed cards, swapped crypto wallet addresses and targeted iPhones on some of the world's biggest websites. Here's how it worked, what an outside scan would and wouldn't have seen, what we're planning, and the rest of a week that also brought a bank outage and a credit union breach.
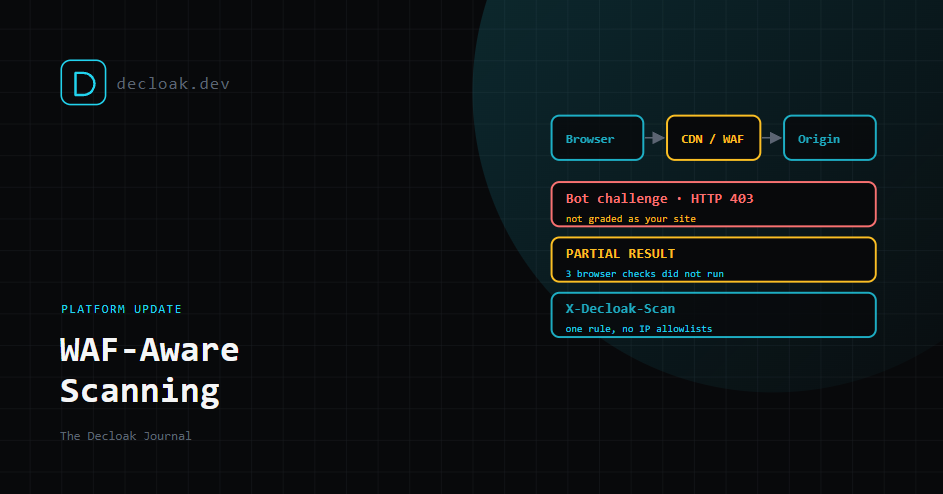
Your Security Grade Might Have Been Grading a Firewall's Challenge Page. Decloak Now Knows the Difference
When a CDN or bot-protection service challenges a scanner, the scanner can end up grading the challenge page instead of your site. Decloak now recognises firewall blocks and challenges, refuses to grade them, shows what sits between visitors and your server, and gives paid teams a private header to let scans through without allowlisting IPs.
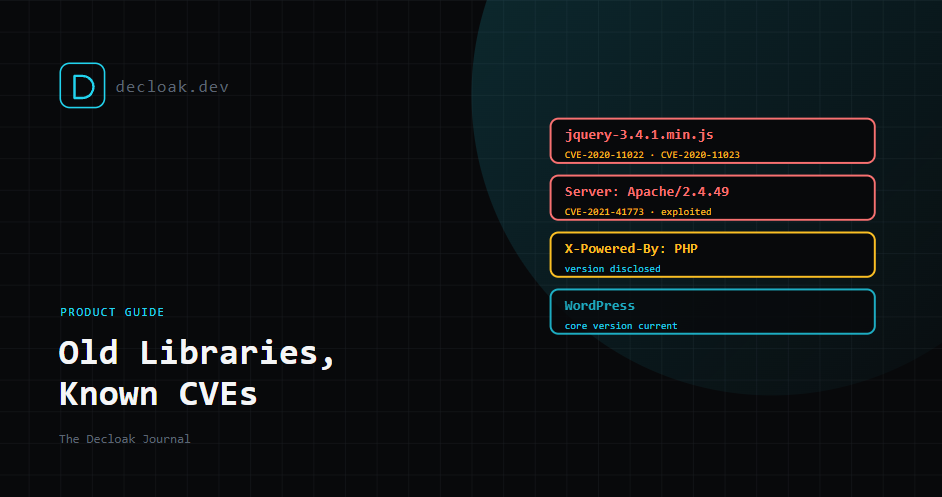
That jQuery You Added in 2019 Is Still Running: How Decloak Finds Vulnerable Libraries and Server Software
Most sites run code nobody has looked at in years: a JavaScript library pinned to an old version, a server announcing its version in every response, a CMS one release behind. Here's how Decloak spots known-vulnerable software from the outside, which databases it checks, and why a match is a starting point rather than a verdict.
Try it now